

Q-Day is the day a quantum computer can break the public-key cryptography that secures most of the internet and every major blockchain. It has no date. It is the moment when hardware meets requirements, and no one knows when that will be.
Should we hold off or start implementing precautions now? Governments and large operators set deadlines years earlier than estimations, because migration still requires work and failure to secure your product can lead to loss of user funds, loss of account access and even the entire control of a product. This guide covers the deadlines that do exist, how far the hardware has to go, and how to plan for Q-Day.
Which quantum deadlines are on the calendar?
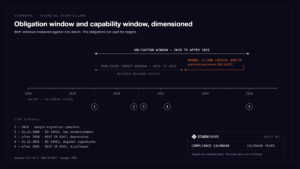
On 22 June 2026 the White House signed Executive Order 14412, which turned years of guidance into fixed deadlines. The order sets 31st December 2030 for post-quantum key establishment on federal agencies’ highest-value systems, and 31st December 2031 for post-quantum digital signatures. CISA and the sector agencies are directed to help critical infrastructure operators do the same.
Other dates sit alongside it. NIST’s transition roadmap, IR 8547, proposes deprecating RSA, ECDSA and ECDH after 2030 and disallowing them after 2035. Google has committed to finishing its own migration by 2029.
None of this is a prediction about Q-Day. They are migration deadlines, based on decision makers’ expectations for Q-Day.
When will Q-Day happen?
Most estimations use one benchmark: a machine that can factor a 2048-bit RSA key in under 24 hours, often called a cryptographically relevant quantum computer. The Global Risk Institute’s 2025 report draws on a survey run annually since 2019. It puts such a machine at 28 to 49 percent likely within ten years and 51 to 70 percent likelihood within fifteen. A wide range from the people who build these machines. The report notes the timeline has accelerated from previous editions.
What has moved faster than the hardware is the size of the target. In 2019 quantum software engineer Craig Gidney and cryptographer Martin Ekerå estimated 20 million qubits and eight hours to break RSA-2048. By 2025 Gidney had the same job under a million, a 20x reduction.
This reduction came from better software, not hardware. Improved circuits need fewer gates, and fewer gates need fewer error-correction cycles and fewer physical qubits. Hardware is improving, but algorithmic progress does not have physical constraints, so the estimations can shrink again next year without a single machine built. AI has accelerated this with activations such as ecdsa.fail allowing anyone to research and improve circuits.
How do you plan for a date nobody knows?
The standard answer comes from co-founder of the Institute for Quantum Computing at the University of Waterloo, Michele Mosca, who reduced the question to three numbers in a 2015 paper. Call them x, y and z. x is how long your secret has to stay secret. y is how long your migration takes. z is how long until Q-Day occurs. If x plus y is greater than z, the information you are protecting today is already exposed, and no amount of precision about z will fix it. Only one of the three is Q-Day, and it is the only one you cannot control.

How far is the hardware from breaking a blockchain?
In March 2026 a team from Google Quantum AI, the Ethereum Foundation, and Stanford published resource estimates on what it will take to break ECDSA, the cryptography behind Bitcoin and Ethereum signatures. The number that matters is about 1,200 logical qubits. A logical qubit is not a physical one: it is one reliable unit assembled from hundreds of error-prone physical qubits. On a superconducting machine, the attack requires fewer than half a million physical qubits, and runs in minutes.
IBM published the most specific plan: Starling aims for 2029 at roughly 200 logical qubits machine, meanwhile Blue Jay expects 2033 to reach a 2,000 logical qubit machine. Against the 1,200 the attack needs, the 2029 machine is six times too small and the 2033 one just clears the bar.
Not all qubits are equal though: between error-correcting codes and architectures, a qubit count says nothing about how long a machine can hold a calculation together. What survives the caveats is the machine’s capability. No machine running in August 2026 is within two orders of magnitude of the required capabilities, and the published targets cross it in the early 2030s.

How long does a migration take?
Many fixes are already complete: NIST finalised ML-KEM, ML-DSA and SLH-DSA in August 2024, and Falcon, standardised as FN-DSA in draft FIPS 206, was first designed in 2017. The main job for every product is implementation.
For a blockchain, implementation timelines depend entirely on where their signature scheme lives. Where they are fixed in the protocol rules, replacing them can require a hard fork or an entire coordinated move of user funds, making the largest hurdles coordination problems, not technical ones. An example of this is BIP-360 implementing quantum resistance in the Bitcoin protocol: technicals are ready, yet no one using Bitcoin today is quantum-secure because there’s no consensus reached to implement BIP-360.
Native account abstraction gives an alternate migration path. Programmable accounts allow post-quantum signatures to be implemented to any account without hard forks: OpenZeppelin has already demonstrated Falcon-512 on Starknet mainnet.
For the proving layer, the migration can be zero. StarkWare’s STARK proofs, which secure Starknet, rely on hash functions such as BLAKE2 rather than elliptic-curve assumptions, so there is nothing in Starknet’s proving layer to migrate. Grover’s algorithm only helps guess which input produced a given fingerprint, so hash-based proofs need larger parameters rather than replacement. SNARKs built on elliptic curves need their commitment scheme replaced with hash-based alternatives.
Settlement requirements range widely, L2s inherit security from settlement and data availability. Their security is entirely dependent on where they settle that data, and for most L2s that is Ethereum. L2s’ dependency on L1s ends one of two ways: either Ethereum migrates to post-quantum signatures, or the L2 becomes an L1 and secures the data itself.
Which chains are ready for Q-Day?
No chain is fully post-quantum today, so it’s worth responding to these claims with a question: safe where? Each chain is different, but all use cryptographic signatures. Each chain can claim quantum-safety in one component and be fully exposed in the next; it only takes one gap to be exposed.
Two properties rapidly reduce migration times: a proof system built on hashes rather than elliptic curves, and accounts that can change their own signature scheme. Starknet was built with both: hash-based proofs and native account abstraction, which gives it structurally lower migration debt than most chains.
This means a shorter migration, not a finished one. The open items are public, all available in our Post-Quantum Hub which breaks down what is live on mainnet from what is still on the roadmap, so you can run that test on Starknet.